Next-Gen AI Security: Beyond Models to Agentic Environments and Continuous Certification
October 5, 2026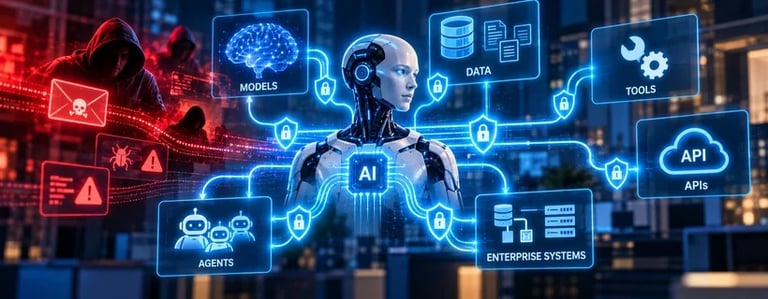

The next wave of AI security centers on agentic workflows and environments, not just the model, since agents interact with tools, APIs, files, datasets, and other agents.
Continuous certification and attestation provide immutable, up-to-date fixes and decisions, with SBOMs and AIBOMs carrying provenance through changes.
Build-time governance restricts each agent with time-bound permissions and production access limits set during construction.
Provenance and risk screening vet provenance and block embedded threats before execution, quarantining risky uploads and screening models, datasets, and inputs for reputation and risk.
Identity and access establish authenticated inter-agent handoffs and map agent relationships, enforcing default-deny controls across users, services, agents, and models.
The threat landscape moves fast: attackers can exploit agentic systems rapidly, including through data poisoning or social hijacking between agents, often before patches exist.
A recap that clarifies why model security alone is insufficient and defines the AIBOM and the key controls for agentic AI security.
Live inventory requires a dynamic, continuous AI Bill of Materials (AIBOM) that inventories every model, dataset, prompt, agent, and tool with provenance and tamper-evidence.
Continuous remediation shifts from periodic patches to autonomous, ongoing fixes while preserving compatibility and avoiding destabilizing changes.
The principle shift is that securing the model isn’t enough; organizations must secure the entire operating environment of agents and their workflows.
Summary based on 1 source
Get a daily email with more AI stories
Source
Security Boulevard • Oct 5, 2026
The Next Wave of AI Attacks Won’t Target Models. They’ll Target Agentic Workflows