Plimsoll: Advanced Sandbox Service Enhances Code Isolation with Multi-Tier Security and Replayable Simulations
October 12, 2026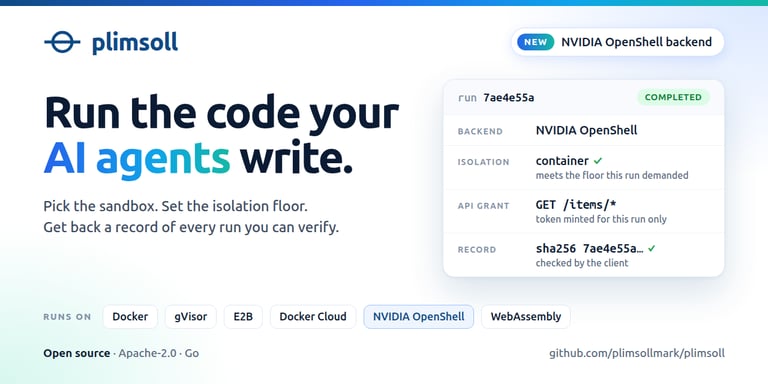

Plimsoll is a sandbox service that runs untrusted, agent-authored code and reports the actual isolation boundary used for each run, offering four tiers from weakest to strongest: process, container, kernel, VM.
Live demonstrations include a cart-pole controller run, with fingerprints showing consistency across runs; live run reports and replayable simulations are accessible on the examples pages.
Documentation outlines isolation tiers, capability grants, run results, sessions, seccomp and gVisor configurations, and deployment workflows, with pre-1.0 status notes and open CI/audit workflows.
The ecosystem provides extensive links to documentation, examples, and integration guides, forming a comprehensive, self-contained platform for running, auditing, and reproducing sandboxed agent code.
The system records run fingerprints as SHA-256 hashes of request and response, and a separate plimsoll-attest tool signs and verifies results; runs can be replayed for verification.
Plimsoll supports multiple providers—WebAssembly QuickJS in wazero process tier, Docker with runsc kernel tier, and Firecracker microVMs in VM tier—and can operate without network access in certain configurations.
An agent framework can integrate with Plimsoll via tools such as Trigger.dev, Vercel AI SDK, Google ADK, Agno/CrewAI, Mastra, and others, enabling code execution in sandboxed environments without exposing credentials.
Requests can specify a minimum isolation floor; if the sandbox cannot meet it, the run is refused and no code executes (ErrInsufficientIsolation).
Summary based on 1 source