CodePulse AI: Revolutionizing DevSecOps with Local-First Security Vulnerability Detection and Remediation
October 28, 2026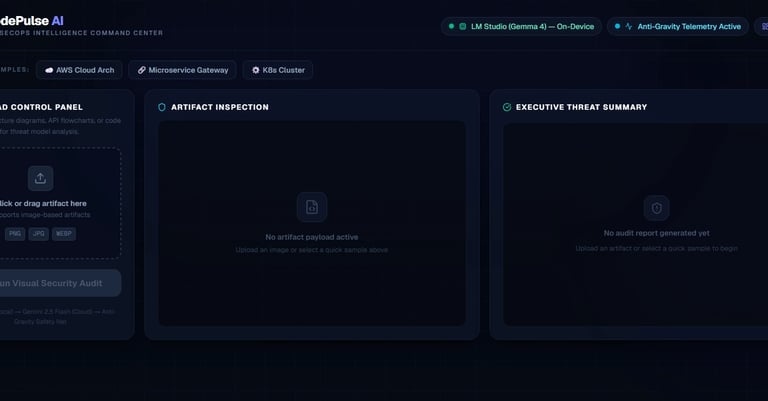

CodePulse AI is an open-source, local-first DevSecOps agent that analyzes architecture diagrams and API flows to identify security vulnerabilities and generates concrete remediation code.
The tech stack for the project blends a Next.js and Tailwind CSS frontend with a FastAPI, Python, Pydantic, and Pillow backend, and uses local Gemma 4 for vision inference with cloud backups as a fallback.
The article is structured with sections like What is CodePulse AI?, Key Features, How It’s Built (Tech Stack), and Demo Workflow, each detailing specific aspects.
In the demo workflow, users drag and drop a microservice diagram into a web dashboard, the system normalizes the image, analyzes nodes, and outputs a threat report with a Security Risk Score and deployable YAML patches.
Key features include private local intelligence, intelligent MIME-type and payload normalization, a tiered fallback engine for high availability, and actionable remediation that writes infrastructure code to fix vulnerabilities.
CodePulse AI is associated with Global Hack Week & Hacktoberfest 2026 Open-Source AI Challenge, with a GitHub repository at https://github.com/AdityaVermaCode/codeplus-ai.
The system combines local vision-language models (Gemma 4 via LM Studio) with a FastAPI backend and a Next.js frontend to enable real-time analysis.
Summary based on 1 source
Get a daily email with more Tech stories
Source
DEV Community • Oct 28, 2026
CodePulse AI: Real-Time Visual Architecture & API Security Auditor 🛡️⚡