Urgent Mitigation Needed for Critical FortiMail Zero-Day Vulnerability Actively Exploited
October 2, 2026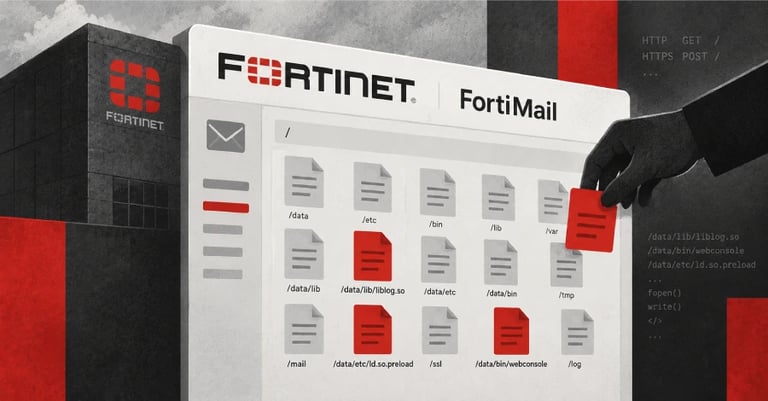

A critical FortiMail zero-day flaw, CVE-2026-104286, is actively exploited with a 9.8 CVSS, allowing unauthenticated arbitrary file writes through path traversal and NULL byte handling weaknesses.
Fortinet’s advisory IDs the root causes as improper pathname restrictions and improper neutralization of NULL bytes, noting exploitation via crafted HTTP/HTTPS requests.
The vulnerability is being tracked in the CVE system and has prompted alerts from CISA, with warnings published as of early October 2026.
Defensive guidance includes limiting internet exposure of management interfaces, isolating management planes, watching ld.so.preload paths, baselining egress, and considering Sigma-based detections for rapid triage.
If a compromise is confirmed, respond with containment: isolate the appliance, preserve evidence, rebuild from trusted images, rotate credentials, and review mail flow rules for unauthorized changes.
Administrators should review attacker-related files, IPs, and log entries to detect any compromise.
Fixes for affected branches are forthcoming, leaving some users on workarounds until patches arrive.
Fortinet provides IOCs and guidance to detect breaches, including suspicious files, configuration changes, and IP indicators.
Additional IOCs are supplied to aid detection and remediation for suspected intrusions.
A set of IOCs helps determine if FortiMail has been compromised and outlines signs of successful attacks.
Remediation involves upgrading to fixed builds and migrating away from FortiMail 7.0, with a documented process to enable faster responses to future advisories.
Temporary mitigations include disabling Identity-Based Encryption or restricting management interface access to trusted networks, using CLI commands, with patches to come.
Summary based on 8 sources
Get a daily email with more Tech stories
Sources
Security Affairs • Oct 2, 2026
U.S. CISA adds Fortinet FortiMail flaw to its Known Exploited Vulnerabilities catalog
The Hacker News • Oct 2, 2026
Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes
SecurityWeek • Oct 2, 2026
Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action
Help Net Security • Oct 2, 2026
Critical FortiMail zero-day exploited in the wild (CVE-2026-104286)