Meta Halts Muse Feature After Security Flaw Exposes Sensitive Chats
October 20, 2026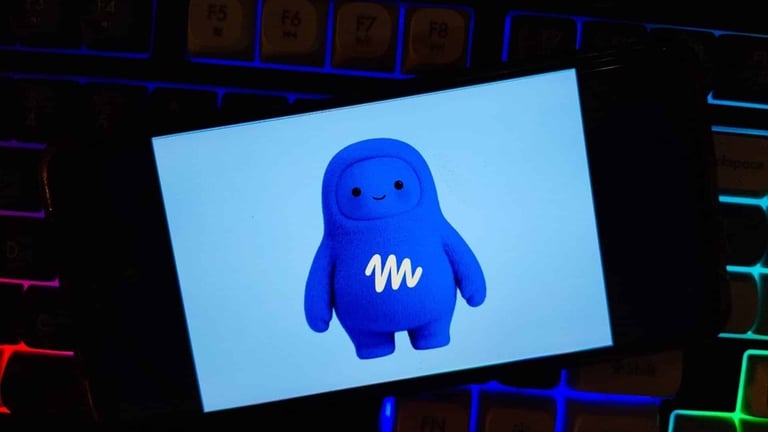

Meta paused Muse's conversation-sharing feature after security researchers found that about 6,800 Muse chat sharing URLs could be exposed through public DNS records, making conversations discoverable like a table of contents.
Claroc opened hundreds of shares and found a mix of unremarkable content and a minority containing sensitive items, including executive-search notes, tax or revenue reviews, a small-business loan application, a bank fraud alert with partial data, a real-estate investor’s performance report, and a workplace vacation calendar.
Claroc noted that the combination of hostname and URL could reveal the nature of the content, enabling reconstruction of the shared page even without the exact link.
Industry context shows rising use of unapproved AI tools for sensitive data, with surveys highlighting policy gaps in how AI-enabled data is handled.
The incident underscores weaknesses in Muse’s link-based access controls and raises broader concerns about data protection and how AI services handle personal information, including data about people who may not use the service.
It also intensifies worries about privacy and user control over data in AI assistants that manage personal and business information.
Meta has not provided guidance on mitigation or response in the excerpt, signaling that further actions may be needed to prevent future disclosures.
Claroc has not found evidence of malicious use yet, but risks include phishing, financial fraud, or impersonation.
Meta’s handling of the incident echoes prior privacy concerns about its technologies and related devices listening or misbehaving in other contexts.
The report recommends concrete HR actions: clearly name and define share links in policies, audit current usage, and determine ownership of AI governance across Legal/IT/HR.
Mitigations include treating Muse as an unapproved app, potentially blocking related domains on managed devices, and briefing recruiters on the issue.
Analysts indicate Muse’s early public rollout has been marred by privacy and security shortcomings, implying ongoing risk and potential further disclosures.
Summary based on 24 sources
Get a daily email with more Tech stories
Sources
ProPakistani • Oct 21, 2026
Meta Suspends Muse AI Sharing Feature Over Privacy Concerns
The Verge • Oct 20, 2026
Meta pauses Muse sharing after researchers find AI chats on the web