Muji Operator Says Up to 27 Million Customer Records May Have Been Exposed
November 12, 2026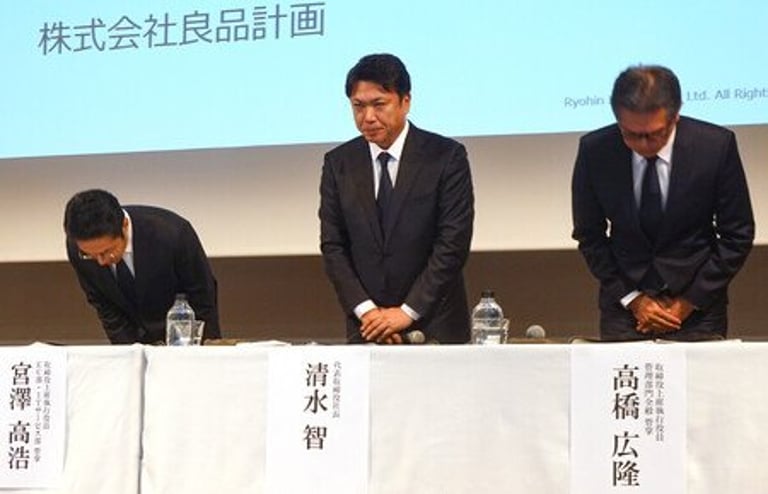

Ryohin Keikaku, the operator of Muji, said it detected unauthorized access on October 29 and believes about 27.26 million customer records, including registered users’ email addresses, may have been exposed.
The incident may also have exposed nearly 1.1 million credit card numbers, including records belonging to former members.
Separately, around 270,000 member accounts were targeted in credential-stuffing attacks using ID and password combinations taken from breaches at other services.
Ryohin Keikaku said it retained full Muji Card numbers after ending their use to identify customers for rewards in July 2021, despite a policy requiring their deletion, and is investigating whether the retention was intentional.
The company acknowledged that the card numbers were not adequately protected and that some former members’ records remained stored beyond the period when they should have been deleted.
At a Tokyo press conference, President Satoshi Shimizu apologized, accepted responsibility and acknowledged shortcomings in the company’s data management.
As a security measure, Ryohin Keikaku suspended its online store.
The company pledged to address system deficiencies and strengthen monitoring, pay the full cost of replacing affected cards and compensate customers for confirmed losses.
Summary based on 3 sources
Get a daily email with more Tech stories
Sources
NHK WORLD • Nov 12, 2026
Muji operator apologizes for data breach
The Japan Times • Nov 12, 2026
Muji operator fails to delete unnecessary credit card data
Nippon.com • Nov 12, 2026
Muji Operator Fails to Delete Unnecessary Credit Card Data